


SOC 2 Compliance & Attestation Services
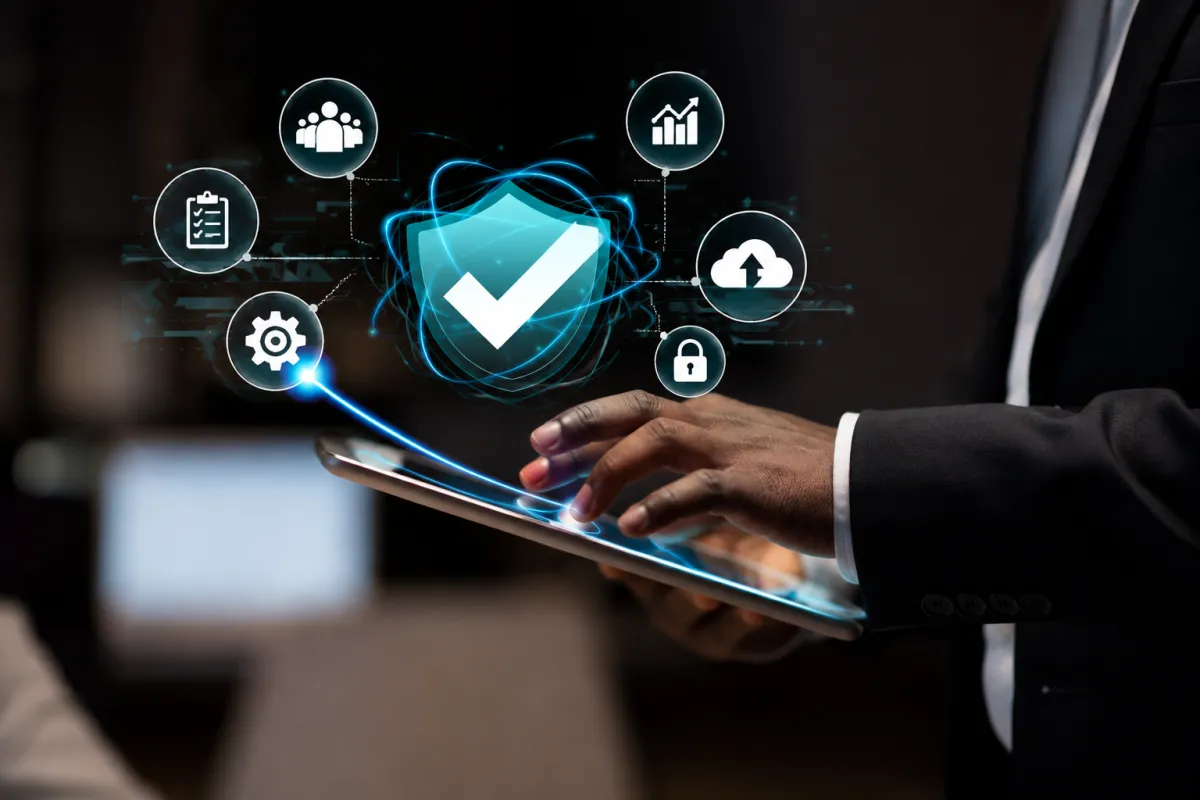
SOC 2 (System and Organization Controls 2) is an internationally recognized attestation framework, developed by the AICPA, that evaluates how effectively a service organization safeguards customer data. Unlike a certification, SOC 2 results in a formal attestation report issued after independent evaluation of controls across security, availability, processing integrity, confidentiality and privacy. For any business that stores, processes or transmits client data, a SOC 2 report is a powerful way to demonstrate trust, transparency and operational discipline to customers, partners and regulators.
WHICH INDUSTRIES NEED SOC 2?
1- SaaS & cloud service providers
2- Data centers & managed IT service providers
3- FinTech & payment processing companies
4- HealthTech & health information platforms
5- HR & payroll service providers
6- Cybersecurity & managed security service providers
7- E-commerce & digital marketing platforms
8- Any B2B vendor requiring third-party data-security assurance
OUR PROCESS
Application & Scoping – Client specifies applicable Trust Services Criteria, systems/locations in scope, and report type (Type I/II).
Contract (CPC) – Proposal and contract issued defining scope, fee, audit type, and timeline; engagement begins on signature.
Stage 1 – Design Evaluation – Auditor reviews existing controls against applicable criteria; gaps documented in a Stage 1 report.
Gap Remediation – Client closes identified gaps within an agreed timeframe before proceeding to Stage 2.
Stage 2 – Formal Audit: (Type I: Confirms controls are suitably designed as of a specific date. Type II: Confirms controls operated effectively over a 3–12-month observation period.)
Fieldwork & Testing – Auditor tests controls via interviews, walkthroughs, and evidence review; exceptions are recorded.
Review & Decision – Audit pack is reviewed and approved by the Certification Decision Committee.
Report Issuance – Formal SOC 2 report issued for distribution to clients/partners, typically under NDA.
Annual Renewal – Re-assessment and a new observation period required each year to keep the report current.
NC Closure – Any exceptions must be remediated and verified within the defined closure timeline before final report issuance.
WHY IT MATTERS
Builds customer trust and competitive differentiation
Often required to close enterprise sales deals, especially in SaaS/B2B
Strengthens internal security posture and risk management
Supports compliance with broader regulatory and contractual obligations
Get in touch with us
Let's connect! Whether you need certification, training, or inspection services, our experts are ready to help. Reach out to us for professional support and seamless solutions.
042-35445641
43-L Abdul Haque Road, Johar Town Lahore.
Monday – Saturday: 10:00 AM – 6:00 PM
READY TO GIVE US A TRY?
Get IFRA Certified Today!
Expand your market and gain consumer trust with Gitchia’s IFRA Certification. Our process is efficient, and ensures full compliance.
Innovation
Driving progress with cutting-edge solutions.
Integrity
Upholding trust through transparency and fairness.
Excellence
Delivering quality and compliance at the highest standards.

FOLLOW US


COMPANY
CUSTOMER CARE
LEGAL
Copyright 2026. Gitchia Institute. All Rights Reserved.